Leçon 1 sur 7 · 8 min
DevSecOps: shifting security left across the lifecycle
DevSecOps makes security part of every stage of building software instead of a final gate. Learn what “shift left” means, what changes at each stage, and the NIST framework that describes it.
Cette page est en anglais pour le moment.
For a long time, software security worked like a customs checkpoint. Developers built a product for months, then handed it to a security team who tested it just before release. Problems found at that point were expensive: code had to be rewritten, deadlines slipped, and sometimes the product shipped anyway with known issues. DevOps made releases faster and more frequent, which made the checkpoint model impossible. You cannot run a weeks-long review before a release that happens several times a day.
DevSecOps is the answer: development, security and operations sharing responsibility for security throughout the software development lifecycle (SDLC). The phrase “shift left” comes from drawing the lifecycle as a line from left (planning) to right (running in production). Shifting left means moving security activities earlier, where problems are cheaper to fix and developers get feedback while the code is still fresh in their minds.
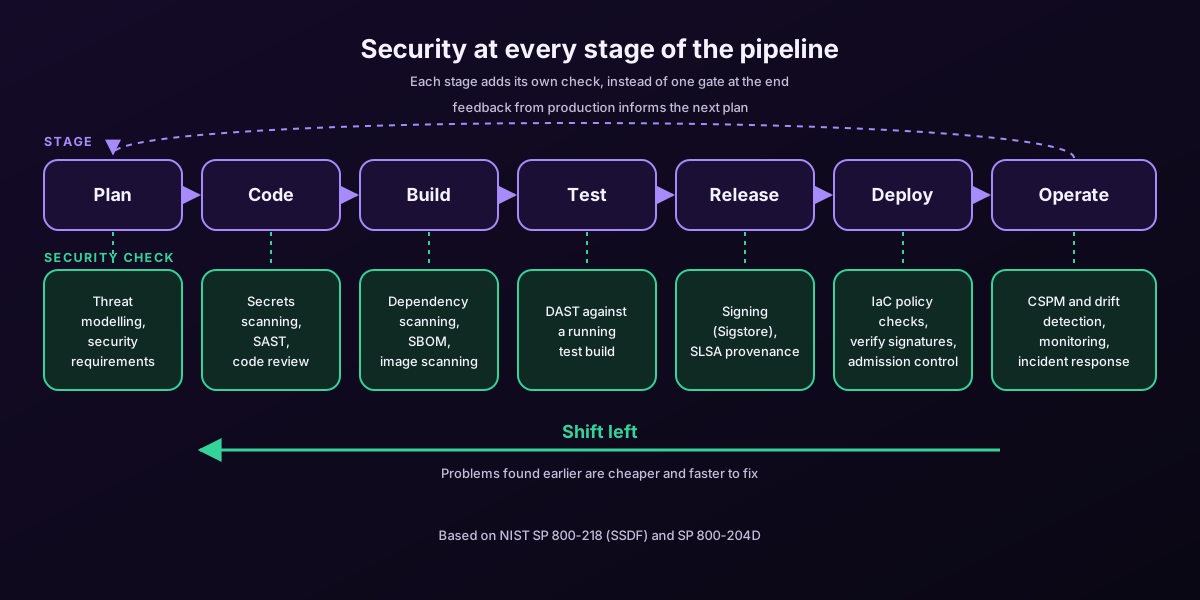
What security looks like at each stage
| Stage | Security activity | Question it answers |
|---|---|---|
| Plan | Threat modelling, security requirements | What could go wrong with this feature, and what must it never allow? |
| Code | Secure coding guidance, secrets detection, code review | Is this change safe, and does it leak anything? |
| Build | Static analysis (SAST), dependency scanning, SBOM generation | Does the code or anything it pulls in have known problems? |
| Test | Dynamic testing (DAST) against a running test build | How does the running application behave when given hostile input? |
| Release | Artifact signing, provenance | Can we prove this artifact is the one we built? |
| Deploy | Infrastructure as code checks, admission policies | Is the environment configured safely before anything goes live? |
| Operate | Monitoring, posture management, incident response | Is it still safe today, and would we notice if not? |
The NIST Secure Software Development Framework
NIST SP 800-218, the Secure Software Development Framework (SSDF), gives these ideas a common structure. It groups practices into four families: prepare the organisation (PO), protect the software (PS), produce well-secured software (PW) and respond to vulnerabilities (RV). The SSDF does not prescribe tools. It describes outcomes, such as “protect all forms of code from unauthorised access and tampering”, which makes it useful for comparing your own pipeline or a supplier’s. NIST SP 800-204D goes further and describes how to build supply chain security into CI/CD pipelines specifically.
Culture matters as much as tools
Shifting left is not the same as dumping security work on developers. Tools that flood a pull request with hundreds of low-value warnings teach people to ignore them. The OWASP DevSecOps Guideline and CISA’s Secure by Design principles both stress that the organisation producing software should own its security outcomes, and that secure defaults beat long checklists.
- Start small: one or two checks that catch real problems, tuned to keep false alarms low.
- Give feedback where developers already work: in the editor and the pull request, not in a separate report weeks later.
- Make the secure path the easy path: templates, pre-approved base images and libraries.
- Name security champions in each team rather than routing everything through one central group.
- Measure time to fix, not only the number of findings.
Where FireAI fits
A developer’s Mac is the first stage of the pipeline: it holds source code, signing keys and access tokens. FireAI protects that machine’s network side. Rules follow each app’s verified code signature, a new app or command-line tool must ask before it connects, and the world map shows where development tools actually send data. It is not a code scanner and does not replace any of the pipeline checks in this course.
À retenir
- DevSecOps shares security responsibility across development, security and operations.
- “Shift left” moves security checks earlier, where fixes are cheaper and faster.
- NIST’s SSDF (SP 800-218) groups secure development practices into PO, PS, PW and RV.
- Good DevSecOps keeps signal high and makes the secure path the easy one.
Vérifiez vos connaissances
1. What does “shift left” mean in DevSecOps?
- Moving servers to another region
- Moving security activities earlier in the development lifecycle — Exact.
- Letting the security team approve every commit
- Dropping production monitoring
Drawn left to right, the lifecycle starts with planning. Shifting left means finding problems earlier, where they cost less to fix.
2. Which NIST publication is the Secure Software Development Framework?
- SP 800-53
- SP 800-218 — Exact.
- SP 800-61
- SP 800-190
SP 800-218 is the SSDF. SP 800-53 is a control catalogue, 800-61 covers incident response and 800-190 container security.
3. Why can a noisy security scanner harm a DevSecOps programme?
- It uses too much disk
- Developers learn to ignore warnings, including the real ones — Exact.
- It makes code run slower
- It is always illegal
Alert fatigue destroys trust. Well-tuned checks that catch real issues are worth more than exhaustive noisy ones.
À vous de jouer avec FireAI
Mettez cette leçon en pratique sur votre propre Mac.
- Règles : appli, site, domaine, IP ou une plage, pour toujours ou jusqu’au redémarrage — Écrivez une règle aussi précise qu’une seule adresse ou aussi large qu’un domaine entier.
- Importez et exportez vos règles — Transférez vos règles vers un nouveau Mac, ou sauvegardez-les, en quelques clics.
- Comment FireAI surveille les connexions de votre Mac — Sachez quelle appli communique avec Internet, en termes simples, sans installer quoi que ce soit qui s’exécute comme un service caché en arrière-plan.
- Listes de menaces (facultatif) — Comparez votre trafic à des données de menaces publiques sans jamais les lui envoyer.
- La Carte du monde — Voyez où vont réellement vos données, pas seulement un nom d’hôte que vous devriez rechercher vous-même.
Sources
- NIST SP 800-218: Secure Software Development Framework (SSDF)
- NIST SP 800-204D: Software supply chain security in DevSecOps CI/CD pipelines
- OWASP DevSecOps Guideline
- CISA: Secure by Design
Mettez-le en pratique sur votre Mac
Essayez toutes les fonctionnalités gratuitement pendant 17 jours, sans carte bancaire.